Most of the conversation about AI and security runs in one direction: the barrier to entry for attackers is collapsing. A teenager with a chatbot can now scan, probe, and exploit at a level that used to require years of practice. That's a real problem, and it deserves the attention it gets.
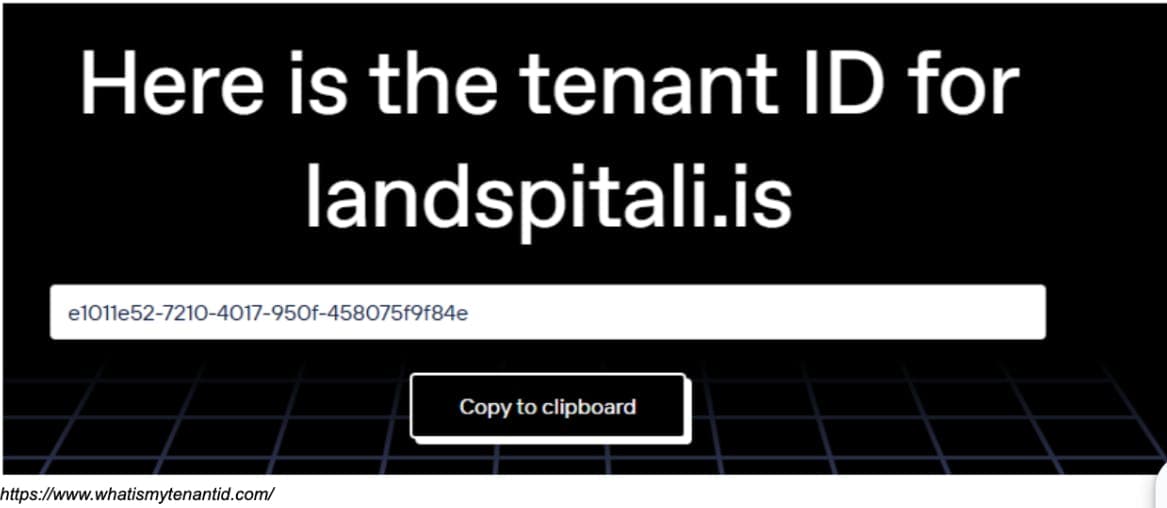
This report details a critical security vulnerability discovered within Landspitalinn's systems through the Defend Iceland bounty program. A series of chained vulnerabilities and misconfigurations were identified, allowing attackers to compromise multiple employee credentials and register multi-factor authentication (MFA) to themselves.
Landspitali is the leading hospital in Iceland and the largest workplace for employees in health care. It is funded by the Ministry of Welfare, supervised by the Directorate of Health and provides specialised and general care and has the capacity of approx. 700 beds. To say that it is an important organisation in Iceland is an understatement and almost every Icelander relies on their services in some way.
One of my favorite methods to gain initial access to companies is finding valid credentials. If your target is just one employee, this might be near impossible. But what if you have hundreds, or even thousands of targets? What if the target victim is anyone in Iceland? Then gaining valid credentials goes from near impossible to near certain.
Organizations evolve through mergers, acquisitions, and rebranding. Old domains get retired, but what happens when those domains can still receive password resets or act as the login email for third-party services for the previous owner? This post reveals an overlooked vulnerability we've seen through Defend Iceland's bug bounty platform: expired corporate domains that remain deeply embedded in third-party SaaS accounts. When these domains become available for registration, attackers can inherit access to SaaS accounts that still use the retired email domain for login or recovery. We'll show you exactly how this happens and why "just let it expire" is a dangerous domain retirement strategy.
Cross-site scripting (XSS) is often treated as a problem that ends at the public perimeter. In reality, customer input does not stop at the landing page. It flows into CRMs, ticketing consoles, and internal dashboards that may never have faced a penetration test. This walkthrough, based on real reports to Defend Iceland, shows how a harmless contact form can compromise the helpdesk staff who read it. To illustrate the chain end to end, we built a Netbankinn-themed lab that mirrors what we see in production environments. The public site is squeaky clean. The internal system is not, and an ezXSS payload turns one support ticket into full access to the staff's browser context.
This post explains a subtle Unicode/Punycode pitfall that can appear in modern authentication flows. It highlights how a normalization mismatch enabled a zero‑click account takeover (ATO) scenario and how to remediate it safely.
This report details a critical security vulnerability discovered within Landspitalinn's systems through the Defend Iceland bounty program. A series of chained vulnerabilities and misconfigurations were identified, allowing attackers to compromise multiple employee credentials and register multi-factor authentication (MFA) to themselves.